Engineering Resilient Cloud Platforms & Supply Chains
Senior DevSecOps & Cloud Platform Engineer
Architecting zero-trust software supply chains (SLSA L3, Sigstore/Cosign, CycloneDX SBOM), multi-cloud enterprise landing zones across Google Cloud, Azure, and OCI, and automated policy-as-code guardrails. Operating GitHub Advanced Security (GHAS) at organization scale with cryptographic provenance and container runtime isolation.


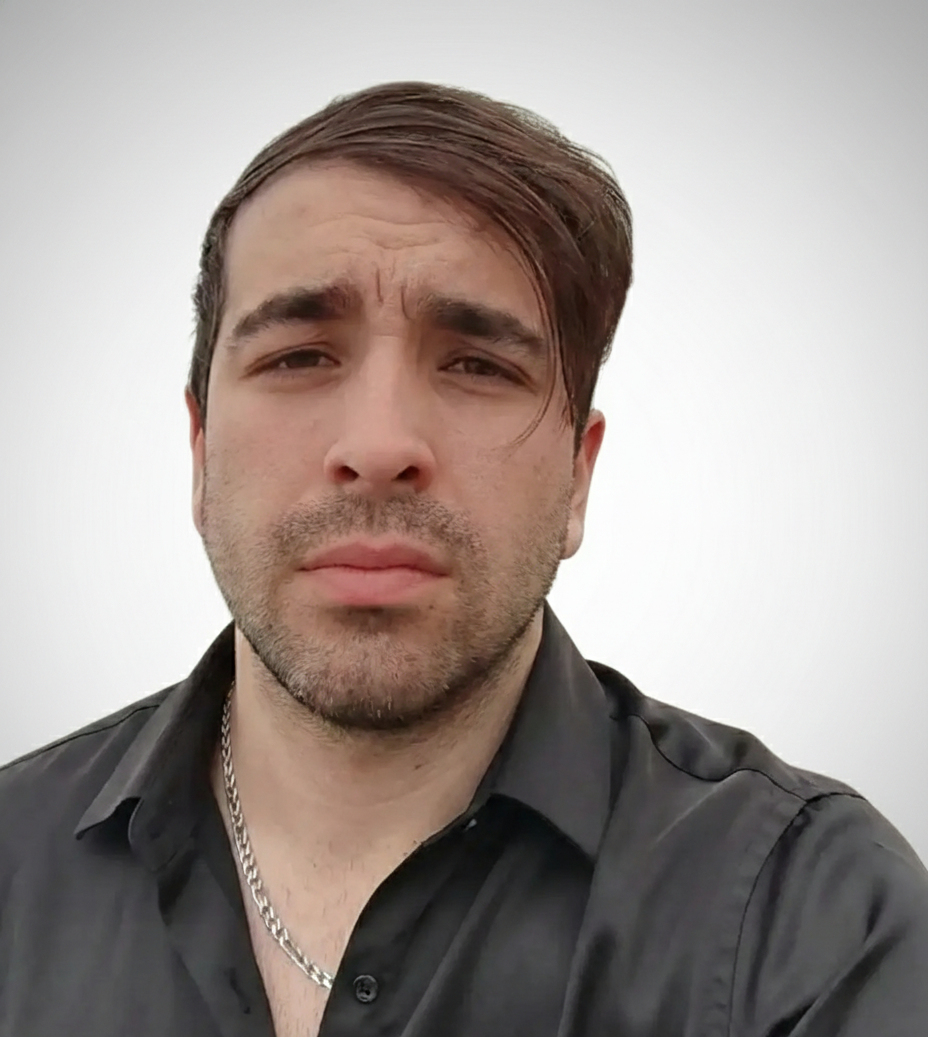
Lautaro Orellano
DevSecOps & Cloud Platform
- CORE SPECIALTY Supply Chain & Cloud IAM
- IDENTITY GOVERNANCE 100% Workload Identity (WIF)
- SUPPLY CHAIN LEVEL SLSA Level 3 Compliant
- MULTI-CLOUD GCP • Azure • OCI
- SECURITY OPERATIONS GHAS Certified Delivery
Operational Impact & Governance Baseline
Measurable technical outcomes delivered across production multi-cloud ecosystems, software supply chain automation, and compliance guardrails.
Zero-Trust Workload Identity Federation Across All CI/CD
Eliminated 100% of static service account JSON keys and client secrets from GitHub repository secrets. GitHub Actions runners authenticate dynamically with GCP and Azure via cryptographic short-lived OIDC tokens (1-hour TTL) mapped strictly to repository, branch, and environment claims.
Cryptographic Provenance & Keyless Attestation
Hermetic container builds signed keylessly with Cosign via Sigstore, paired with automated CycloneDX SBOM generation and in-toto attestations published directly to OCI registries.
Remediation SLA for Critical & High CVEs
AST taint tracking via custom CodeQL query suites prioritizing reachability over raw alert counts. Dependabot grouping configurations and automated patch PR verification reduce developer alert fatigue and slash remediation velocity.
Automated Landing Zones & Shared VPC Topologies
Hub-and-Spoke Shared VPC architecture in GCP isolating Core Network, Security Operations, and Workload Projects. Hardened with Cloud NAT egress-only routing, Cloud Armor WAF with OWASP Core Rulesets, and zero primitive IAM roles.
Interactive Architecture Studio
Production-grade reference architectures designed for enterprise environments. Select a blueprint to inspect the topology, operational flow, and technical controls.
SLSA Level 3 Supply Chain & Cryptographic Provenance
Eliminating supply chain tampering through hermetic build pipelines, AST taint analysis, keyless artifact signing with Sigstore, and in-cluster admission policy enforcement.
permissions: contents: read, id-token: write
Modern pipelines suffer from dependency confusion, poisoned third-party build actions, unverified container registries, and runtime deployment of unvetted binaries directly into production Kubernetes clusters.
- Third-party GitHub Actions pinned strictly to full 40-character commit SHAs.
- Distroless minimal runtime base images eliminating bash, apt, and curl.
- Kubernetes admission controller rejects pods with Critical CVEs or unsigned digests.
Multi-Cloud Enterprise Landing Zone & Shared VPC
Centralized network security governance, automated Terraform infrastructure modules, Cloud Armor WAF filtering, and OIDC federation across Google Cloud, Azure, and OCI.
Hub-and-Spoke • Zero Public IPs on Compute
Uncontrolled cloud sprawl causes exposed public IPs on backend workloads, primitive Owner/Editor roles granting excessive privileges, uninspected egress, and disjointed identity management.
- Backend compute clusters are completely private, egressing only through Cloud NAT.
- Terraform remote state isolated in encrypted Cloud Storage with object locking.
- Azure DevOps to GitHub migration credentials for enterprise workload transitions.
Policy-as-Code Guardrails & Automated IaC Gating
Validating Terraform execution plans before merge using Open Policy Agent (OPA/Rego) and Checkov, shifting compliance enforcement directly into developer pull requests.
terraform plan • Conftest / OPA • Fail-Fast
Manual peer reviews of massive Terraform PRs miss security misconfigurations (unencrypted S3/GCS buckets, 0.0.0.0/0 on SSH ports, public database replicas), discovered only during quarterly audits.
- Hard blocker on any firewall rule allowing 0.0.0.0/0 ingress on ports 22, 3389, or 5432.
- Mandatory Customer Managed Encryption Keys (CMEK) on all object storage.
- Rego policies maintained in central governance repo, pulled dynamically in CI.
Architecture Decision Records (ADRs)
Documented production trade-offs, security rationales, and architectural decisions adopted across cloud platforms and CI/CD operations.
Workload Identity Federation (WIF) vs Static Service Account JSON Keys
Storing permanent service account JSON keys in CI repository secrets introduces severe leak vectors, zero automatic revocation, and massive rotation friction across dozens of repositories.
Enforce Workload Identity Federation (OIDC) between GitHub Actions and GCP/Azure. Short-lived tokens (max 1 hour TTL) are exchanged based on strict repository and branch claims.
100% elimination of stored cloud credentials; token compromise scope is limited to 1 hour; full auditability via Cloud Audit Logs.
Centralized Reusable Workflows vs Distributed Composite Actions
Teams duplicated security pipeline configurations, leading to drifting scanning tool versions (CodeQL, Dependabot) and fragmented compliance auditing across repos.
Standardize on centralized reusable workflows (workflow_call) hosted in a hardened .github organization repository with mandatory required status checks.
Organization-wide rollout of security updates in a single commit; streamlined compliance auditing; clean declarative caller workflows.
Hub-and-Spoke Shared VPC vs Full Mesh Peering for GCP Isolation
Managing independent VPCs per workload project with VPC peering creates exponential network connections, risking non-transitive route limits and CIDR overlaps.
Implement Shared VPC with a central Host Project managing subnets, Cloud NAT, and Cloud Armor WAF. Service Projects attach to delegated subnets without network admin privileges.
Centralized network security perimeter; unified Cloud NAT egress gateways reducing cost; strict separation between platform engineers and developers.
In-Cluster Admission Control (Kyverno) vs CI-Only Validation
Relying solely on CI pipeline scanning leaves Kubernetes clusters vulnerable to manual kubectl apply overrides, compromised registries, and unvetted Helm charts.
Deploy Kyverno validating admission webhooks in Kubernetes clusters to enforce Sigstore/Cosign signature verification and reject root execution (runAsNonRoot: true).
Non-bypassable perimeter at cluster entry; unsigned or tampered containers cannot execute regardless of deployment source.
Core Operational Disciplines
Deep technical focus areas across application security, multi-cloud platforms, container isolation, and threat modeling.
Operating GitHub Advanced Security (GHAS) at organization scale. I architect CodeQL pipelines utilizing customized query suites and AST taint-tracking models that analyze data flows from untrusted inputs to critical sinks (SQL injection, SSRF, path traversal, deserialization).
Secret scanning with push protection is strictly enforced with regex patterns tailored to proprietary token formats, ensuring high-entropy credentials never hit Git history. Dependabot operates with structured grouping rules to minimize developer alert fatigue while auto-merging patch bumps verified by green test suites.
Designing automated infrastructure baselines with Terraform. On Google Cloud Platform, I engineer Shared VPC network fabrics, configure Cloud Armor WAF rate-limiting policies, and structure Cloud IAM using least-privilege predefined roles instead of legacy primitive roles.
On Microsoft Azure, I focus on enterprise migrations, leveraging partner delivery credentials for translating Azure DevOps pipelines, boards, and artifacts into hardened GitHub Actions. On Oracle Cloud Infrastructure (OCI), I implement compartment hierarchies, VCN security lists, and identity domain policies.
Container isolation begins at image build: utilizing multi-stage Dockerfiles and Google distroless or Alpine minimal bases to eliminate package managers, shells, and unnecessary utilities from final production artifacts, reducing attack surfaces by over 80%.
Inside Kubernetes clusters, workloads adhere to the Pod Security Admission (PSA) restricted profile: enforcing non-root execution (runAsNonRoot: true), dropping all Linux capabilities (capabilities: drop: [ALL]), read-only root filesystems (readOnlyRootFilesystem: true), and restrictive NetworkPolicies enforcing default-deny ingress and egress.
Security is driven proactively via architectural threat modeling during early RFC phases. Utilizing the STRIDE methodology, systems are analyzed for spoofing, tampering, repudiation, information disclosure, denial of service, and elevation of privilege before code is written.
On the observability layer, Cloud Audit Logs, VPC Flow Logs, and Kubernetes audit streams are routed to centralized SIEM / telemetry stacks (Prometheus, Grafana, Alertmanager), aligned with CIS Cloud Benchmarks and NIST 800-53 security controls.
Operational Toolchain Ecosystem
Production tooling structured across the application lifecycle, cloud infrastructure, and security validation.
AppSec & Supply Chain
AST taint tracking, keyless container signing, CycloneDX SBOM generation, push protection secret scanning.
Cloud Platforms
Landing Zones, Shared VPC networking, Cloud Armor WAF, Workload Identity Federation, kernel security hardening.
IaC & Policy-as-Code
Modular multi-cloud infrastructure, pre-merge plan validation, compliance guardrails enforcing encryption and network isolation.
Containers & Runtime
Rootless execution, Pod Security Admission restricted profile, admission webhook signature verification, NetworkPolicies.
Observability & SecOps
Cloud Audit Logs aggregation, GHAS vulnerability triage dashboards, CIS Benchmark drift detection, automated routing.
Automation & Scripting
Custom CI/CD tooling, automated alert triage scripts, cloud API integrations, and declarative workflow pipelines.
Verifiable Credentials & Certifications
Official certifications and delivery credentials validating competence across GitHub, Google Cloud, Microsoft Azure, Oracle Cloud, and the Linux Foundation.
 Foundations
 Actions
 GHAS Certified
 Security Delivery
 Copilot Delivery
 Migrations Delivery
 ADO Migrations
 Security Sales
 Copilot Sales
 Sales Pro
 Platform Sales
 Revenue Motions
 Technical Sales
 Foundations
 Terraform on GCP
 Cloud Security Network
 Network Dev
 Load Balancing
 ML Data Prep
 App Dev Env
 AZ-900 (In Progress)
 OCI Cloud Foundations
 Linux Intro (LFS101)
